> For the complete documentation index, see [llms.txt](https://dev-angelist.gitbook.io/crtp-notes/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://dev-angelist.gitbook.io/crtp-notes/readme/system-security-1/1.3-logical-components-of-ad.md).
# 1.3 - Logical Components of AD
## **AD DS Schema**
\
The schema defines the structure and rules for objects stored in Active Directory. It is critical for maintaining consistency and ensuring the directory can adapt to organizational needs.
### **Key Features**
* **Object Classes**:\
Define entities like users, computers, and groups. For example, a "User" object class includes attributes such as `Username`, `Email`, and `Group Membership`.
* **Attributes**:\
Specify properties of objects. Each object class has mandatory and optional attributes.
* **Extensibility**:\
Administrators can extend the schema to include custom attributes or object classes as business requirements evolve.
* **Replication**:\
Schema updates are replicated across all domain controllers in the forest to ensure uniformity.
* **Practical Example**:\
When deploying a custom application, you might extend the schema to include new attributes (e.g., "Application License Key") tied to user accounts.
## **Domains**
\
Domains are foundational units in AD, providing a centralized boundary for management, security, and replication.
### **Key Features**:
* **Organizational Boundary**:\
Each domain groups objects under a shared namespace (e.g., `example.com`).
* **Security Boundary**:\
Domains enforce access control and authentication policies, ensuring users only access permitted resources.
* **Trust Relationships**:\
Enable collaboration across domains while maintaining distinct security boundaries.
* **Namespace Management**:\
DNS integration allows resources to be easily discovered and accessed.
**Real-World Usage**:\
A multinational organization might have separate domains for each region (e.g., `europe.example.com`, `asia.example.com`), each with its administrative team and policies.
## **Trees**
\
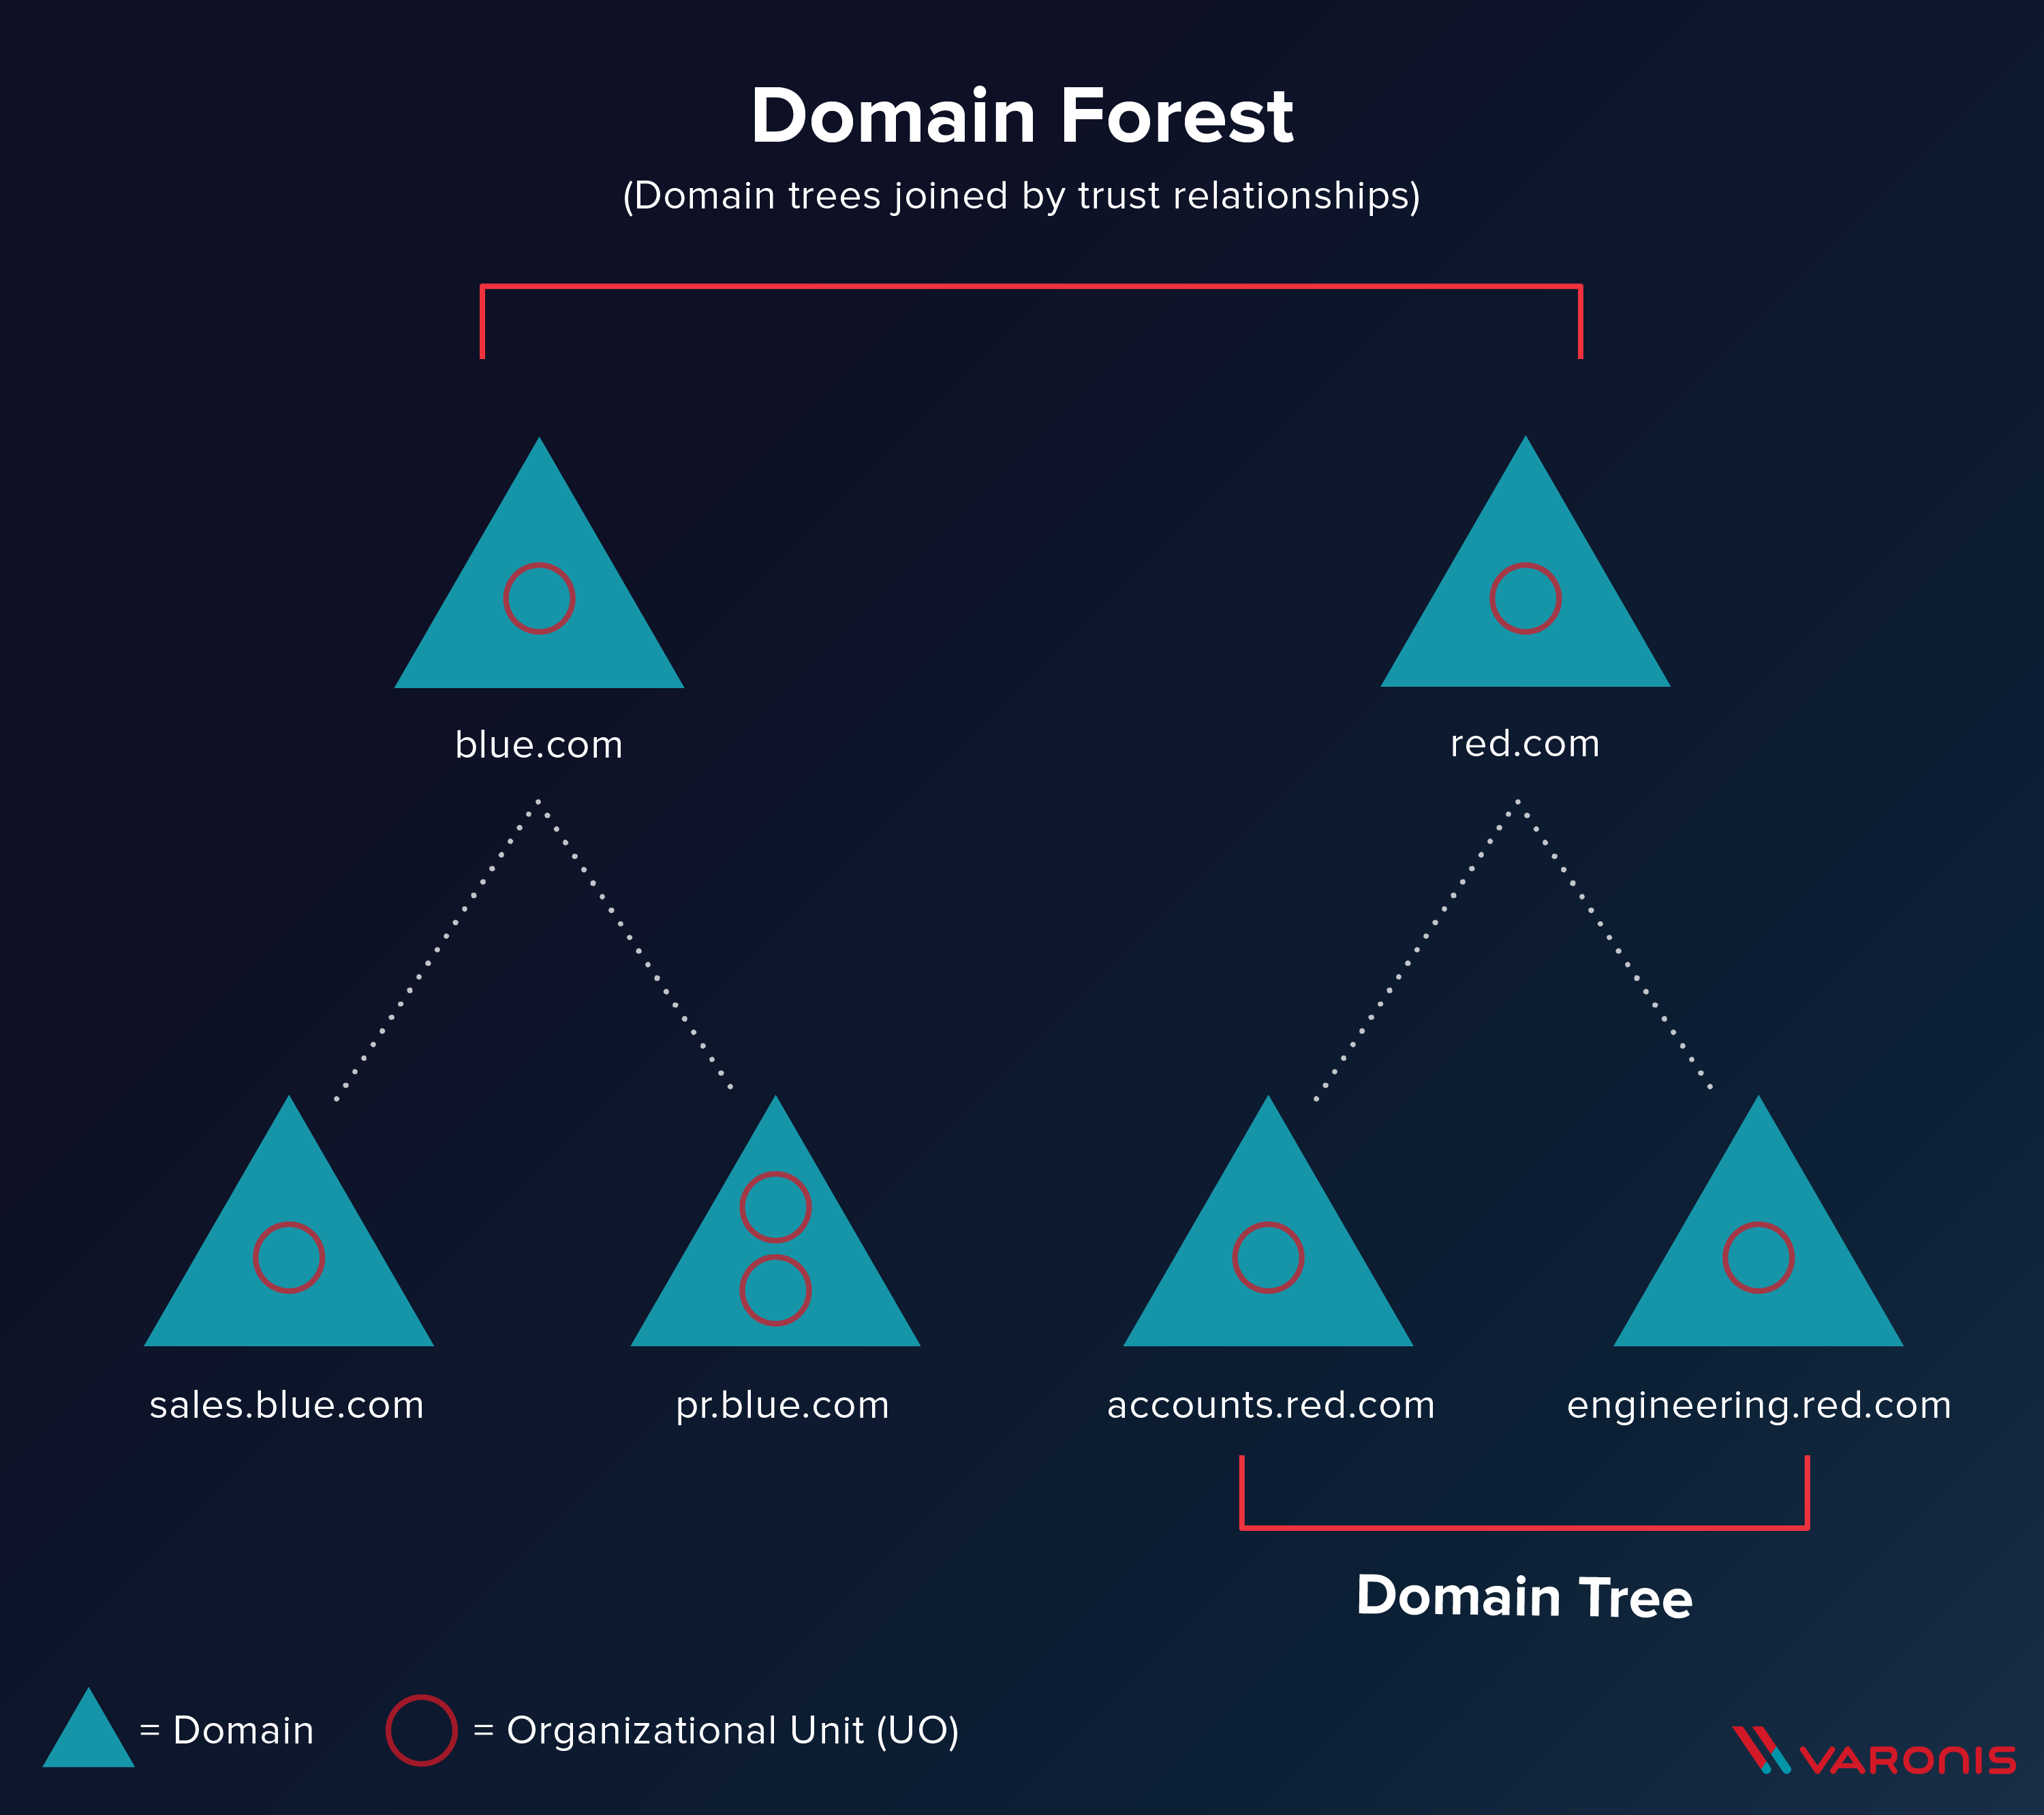
A tree is a hierarchical structure comprising a parent domain and its child domains, sharing a contiguous namespace.
### **Key Features**
* Domains within a tree automatically trust each other through transitive trust relationships.
* Useful for managing organizations with multiple departments or geographic locations while maintaining a unified structure.
## **Forests**
\
Forests represent the top-level logical boundary in Active Directory. A forest can contain multiple trees, each with distinct namespaces, but sharing the same schema and Global Catalog.
### **Key Features**
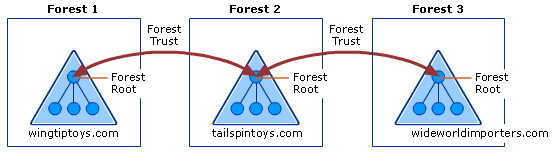
* Acts as the ultimate security boundary; inter-forest communication requires explicit trust configurations.
* Forest-wide policies apply uniformly across all domains.
## **Organizational Units (OUs)**
\
OUs are containers within domains used to organize objects logically for administrative purposes.
### **Key Features**
* Allow delegation of administrative responsibilities without granting full domain-level access.
* Enable application of specific Group Policy Objects (GPOs) to subsets of users or computers.
**Example**:\
A company might create separate OUs for "Finance," "HR," and "IT," each with tailored policies and administrative controls.
## **Trusts**
\
Trusts allow users in one domain or forest to access resources in another securely.
### **Types**
* **Transitive Trusts**: Automatically established within a forest.
* **External Trusts**: Configured between forests or standalone domains.
**Practical Use**:\
Trusts are essential for mergers or partnerships where resource sharing is needed while retaining separate administrative boundaries.
## **Objects**
Objects are the individual elements within AD, representing entities like users, groups, computers, and printers.
### **Key Features**
* Each object belongs to a specific class and is identified by a unique name (e.g., a user's `samAccountName`).
* Attributes define the characteristics and functionality of objects.
## **Forests and Domain Trusts**
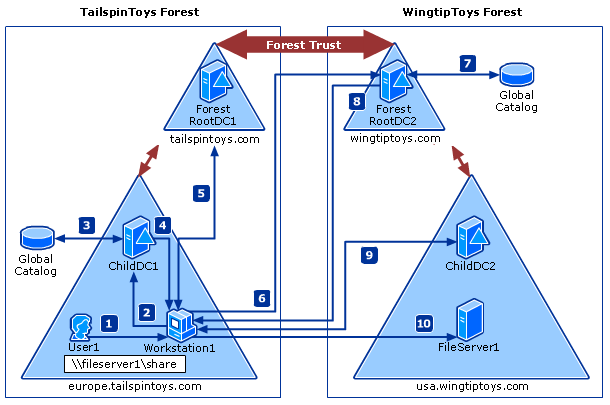
Trust configurations extend collaboration and resource sharing across forests.
**Complexity and Security**:\
Managing trust relationships requires careful planning to avoid unintended access or security gaps.
## Difference between OUs and Security Groups
**OUs (Organizational Units)** are used to organize and manage objects (like users and computers) within a domain. They help with delegating administrative tasks and applying group policies but don’t control access to resources.
**Security Groups** are used to manage access to resources, such as files or applications. Users are grouped based on the permissions they need, and access is granted based on group membership.
**Example**: You could have an OU called "HR" to manage HR users, while a "Finance" Security Group might control access to sensitive financial files. OUs organize, while Security Groups manage permissions.