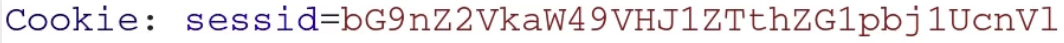> For the complete documentation index, see [llms.txt](https://dev-angelist.gitbook.io/ewptxv3-notes/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://dev-angelist.gitbook.io/ewptxv3-notes/readme/5.5-other-common-web-attacks/5.5.1-session-attacks/6.2.3-session-hijacking-via-cookie-tampering.md).
# 6.2.3 Session Hijacking via Cookie Tampering
## **Cookie tampering**
{% embed url="" %}
**Cookie tampering** is a method in which the attacker manipulates or modifies the information of the stored data on a web browser. This includes all types of data like personal information (name, number, address), and credentials for certain websites, or it can be the settings for specific websites. it is intended to steal valuable information from users.
We can capture a cookie (usually encoded in Base64) using Burp Suite,
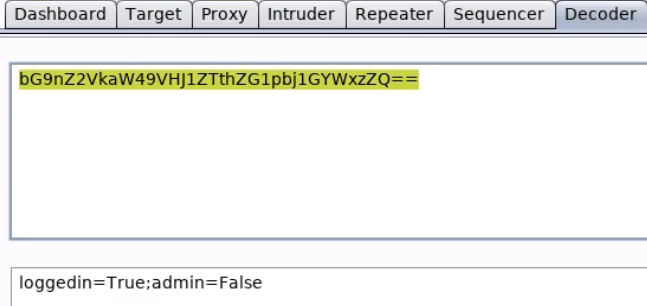
and decode it in plain text using Decoder:
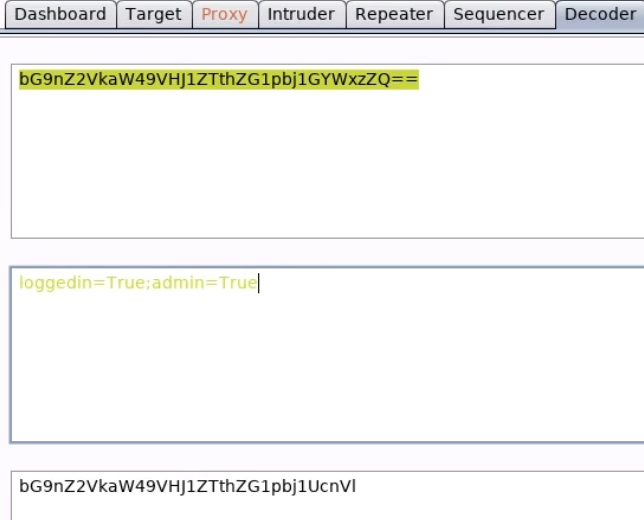
Seeing it, we quickly understand that we're log in, and we've not admin permission, then we can change value of admin to 'True' and encoding again it in Base 64:
Now that we've setted session id with admin privileges, we can use repeater to use this custom session id value and login in into privileged account.